


DevOps, cloud and IT support services
Deployments that run themselves, servers that stay up, teams that get answers.
DevOps, DevSecOps, cloud, system administration and IT support: we automate your deployments, secure your pipelines, run your servers and look after your users. From a single VPS to a Kubernetes cluster, with the host of your choice.
What we deliver, concretely.
Continuous delivery (CI/CD)
Every commit tested, built and deployed automatically with GitLab CI, GitHub Actions or Jenkins. No more Friday-evening releases by hand.
Infrastructure as Code
Servers, networks and DNS described with Terraform, OpenTofu and Ansible: the infrastructure can be read, versioned and rebuilt exactly as it was.
Containers and orchestration
Docker, Docker Compose, Kubernetes or k3s, Helm and Argo CD: the application runs the same way locally, in staging and in production.
Security inside the pipeline
Secrets caught before the commit, dependencies and images scanned, code analysed with Gitleaks, Trivy, SonarQube and Semgrep. A flaw is stopped before it ships.
Cloud, servers and backups
Linux servers, virtualisation, reverse proxies, databases, high availability, backups and a recovery plan. And a cloud bill brought back down.
IT support and workstations
Accounts and access, Microsoft 365 or Google Workspace, email, VPN and network, requests tracked in a ticketing tool: your teams know who to write to.
Four steps, one firm price.
Four domains, and the tools we use in each.
DevOps
CI/CD automation, continuous delivery, Infrastructure as Code, containerisation, orchestration, task automation, monitoring and observability.
 GitLab CI/CD
 GitHub Actions
 Jenkins
 Docker
 Compose
 Kubernetes
 k3s
 Helm
 Argo CD
 Terraform
 OpenTofu
 Ansible
 Bash
 Python
 Prometheus
 Grafana
Loki
DevSecOps
Security built into the pipelines: code analysis, secret detection, vulnerability scanning, container hardening, secret management and access control.
 Trivy
 SonarQube
Semgrep
 OWASP ZAP
 Snyk
 HashiCorp Vault
Cloud & SysAdmin
Designing and running infrastructure: Linux servers, virtualisation, web hosting, DNS, reverse proxies, databases, high availability, backup, disaster recovery and cloud cost tuning.
 AWS
 Google Cloud
 OVHcloud
 Hetzner
 Scaleway
 DigitalOcean
 Vultr
 Linode (Akamai)
 IONOS
 Cloudflare
 Linux
 Proxmox VE
 VMware
 Nginx
 Caddy
 HAProxy
 PostgreSQL
 MySQL
 MongoDB
 Redis
Restic
Proxmox Backup Server
 Active Directory
IT support & assistance
User support, incident diagnosis, workstation administration, account and access management, network assistance, business email, documentation and guidance.
 Windows
Linux
Microsoft 365
Google Workspace
Microsoft Entra ID
GLPI
Zammad
 RustDesk
 WireGuard
 MikroTik
 pfSense
 OPNsense
Zabbix
What we have put in place, for our clients and for ourselves.
Deploying and running containerised applications, Kubernetes monitoring, MySQL performance tuning and backups.
Kubernetes
Docker
GitLab CI/CD
MySQL
BunkerWeb (WAF)
Portabase
Beszel
A study of how to secure access to the monitoring and backup interfaces, and to phpMyAdmin.
Cloudflare Zero Trust
Cloudflare Tunnel
Running the backend's deployment environment, setting up the CI/CD pipeline and hardening the deployment server.
Docker
Nginx
Linux
MySQL
iptables
 Hostinger
Diagnosing an SMTP incident, following up the suspension of outgoing mail with the host, and reviewing the Next.js environment.
 Next.js
 Node.js
SMTP
Several application services, staging environments, a PostgreSQL instance dedicated to AI agents, automated deployment and protection of sensitive data.
Docker
GitLab CI/CD
PostgreSQL
 FastAPI
MongoDB
HashiCorp Vault
MySQL
A virtualised environment, network segmentation, routing and automated provisioning of GitLab CI runners.
Proxmox VE
Terraform
Ansible
OPNsense
GitLab CI/CD
Automated switchover between two versions of an application, with a rollback ready, and no Kubernetes.
Docker Compose
Python
Nginx
Metric collection, dashboards, alerts and uptime tracking.
Prometheus
Grafana
 Uptime Kuma
Beszel
Dozzle
Centralised logs, to diagnose an incident in minutes rather than hours.
Loki
 Graylog
 Filebeat
Scheduled backups, retention management and restores prepared in advance.
 Stockage S3
Bash
Remote access over VPN, an SSH bastion and separated environments.
WireGuard
 Guacamole
OpenSSH CA
HashiCorp Vault
Warpgate
Containerised applications, service management and reverse proxy configuration.
Docker Compose
Linux
Nginx
Caddy
An AI-assisted workflow for reviewing and sorting applications.
 n8n
 API OpenAI
3 projects, in production.
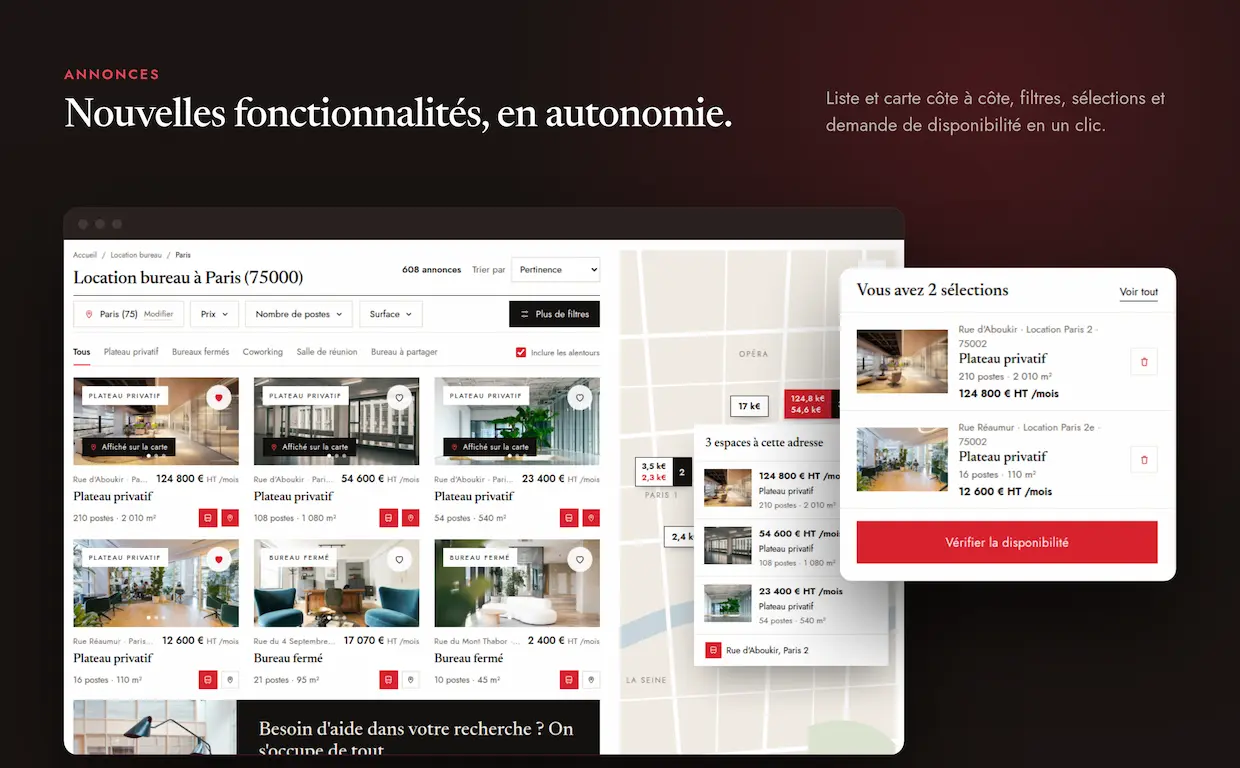
Urbidesk
Office rentals: new features, SEO, an internal CRM and AI-automated prospecting.
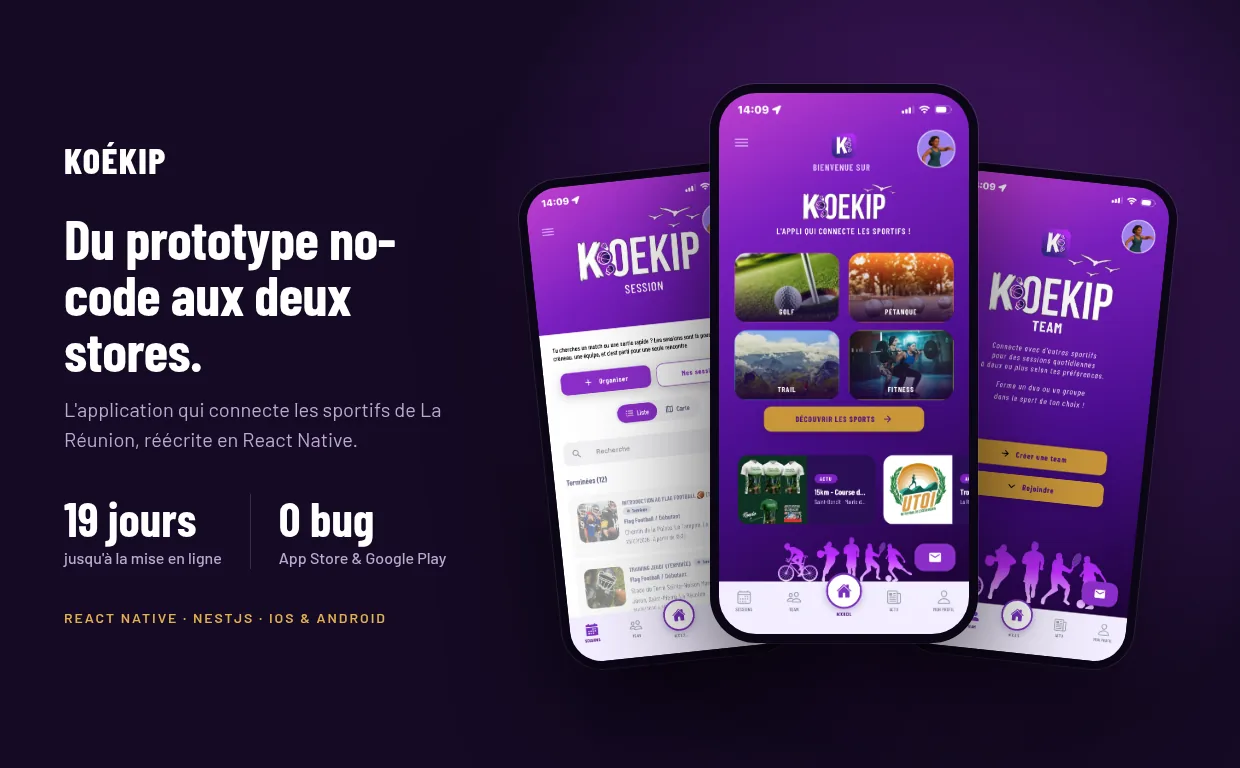
Koékip
A no-code prototype rewritten as a React Native app, published on both stores in 19 days.
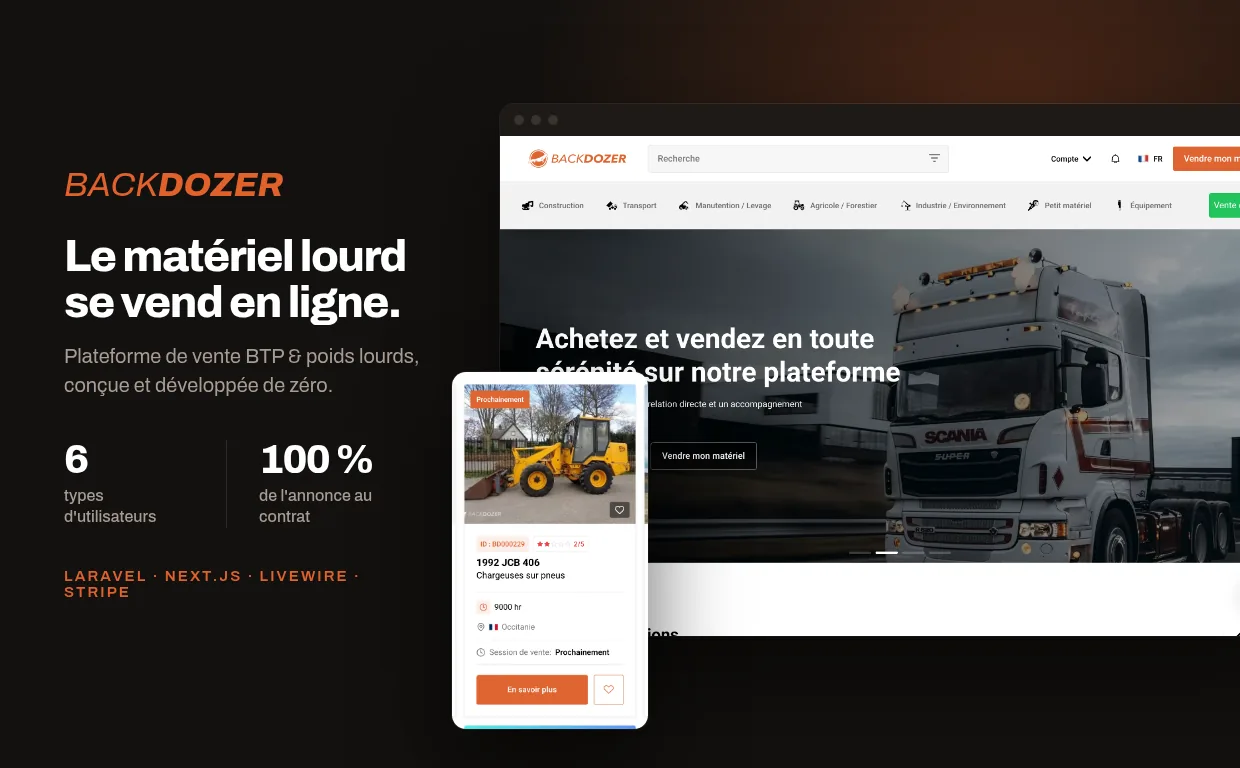
Backdozer
A marketplace built from scratch: six profiles, sliding-scale sales, transport, payment and contracts.
Where this service already runs.
What we get asked before signing.
DevOps automates building, testing and deployment. DevSecOps adds security checks at every step: secret detection, dependency and image scanning, code analysis. A flaw is stopped in the pipeline instead of being found in production.
Not necessarily. For one or two applications, Docker Compose on a well-kept server is often enough. Kubernetes or k3s earn their place when services multiply or when the application has to survive a server failure. We say so at the audit, with the costs to back it up.
Often. Oversized instances, forgotten resources, storage never purged: the audit puts a figure on what can be cut or moved, including to a European host such as Hetzner, Scaleway or OVHcloud.
Yes. Accounts, access, email, Windows or Linux workstations, VPN: we work remotely and track every request in a ticketing tool such as GLPI or Zammad. One to two hours ahead of Paris, we share your working day.
An NDA signed before any access, named accounts, rights limited to what is strictly needed, secrets kept in a vault such as HashiCorp Vault and never in the code. The access stays yours, and is revoked when the engagement ends.
Describe the problem. We send back a costed proposal within 48 hours.
Scope, firm price and delivery date, in the contract. NDA signed before the first technical conversation.